Blog

  • How to Protect AI API Keys and Other Secrets on a Website Host

    How to Protect AI API Keys and Other Secrets on a Website Host

    How to Protect AI API Keys and Other Secrets on a Website Host

    Answer box:
    Store AI API keys, database passwords, webhook signing secrets and similar credentials server-side only: in your host’s secret store, a cloud secret manager, or server environment variables that are injected into the runtime. Do not put them in browser JavaScript, public repositories, theme files, client-side environment variables, screenshots, support tickets, or logs. For WordPress, prefer a plugin that reads a key from wp-config.php, an environment variable, or your host’s secret manager; if a plugin stores the key in the database, assume WordPress administrators and some plugins may be able to access it. If a key leaks, revoke or rotate it immediately, update every place that uses it, review logs and billing, and remove the exposed value from code, logs and tickets.

    1. Know what counts as a secret

    A secret is any value that lets software authenticate, sign, decrypt, impersonate, spend money, read private data, or change infrastructure. For an AI-assisted website, that usually includes:

    • AI provider API keys.
    • Database usernames, passwords and connection strings.
    • Webhook signing secrets for payments, forms, CRM tools or deployment hooks.
    • SMTP passwords and transactional email API tokens.
    • Object storage keys.
    • WordPress salts, application passwords and private plugin license keys when they unlock privileged features.
    • SSH private keys, deploy keys and CI/CD tokens.

    Treat a secret as compromised if it appears in a Git commit, browser bundle, HTML source, JavaScript console, analytics payload, crash report, server log, debug file, screenshot, chat transcript, plugin support ticket or public paste. OpenAI’s current API documentation states that an API key is a secret, should not be shared or exposed in client-side code, and should be loaded from an environment variable or key management service on the server. (developers.openai.com)

    The practical rule is simple: configuration that is safe for visitors to see can be public; credentials must stay on the server side.

    2. Never put AI API keys in browser-side code

    A browser is not a private place. Anything sent to the browser can be inspected by the visitor, copied by extensions, captured by proxies, cached, or discovered in built JavaScript files. That includes “hidden” fields, frontend framework variables, minified bundles and source maps.

    OpenAI’s API key safety guidance says not to deploy keys in client-side environments such as browsers or mobile apps, and recommends routing requests through your own backend server instead. (help.openai.com) Next.js documentation gives a concrete example of why naming matters: variables prefixed with NEXT_PUBLIC_ are inlined into the JavaScript bundle delivered to the browser, while non-public variables remain available only in the Node.js environment. (nextjs.org)

    A safe architecture looks like this:

    1. Visitor submits a form or chat message in the browser.
    2. Browser calls your own endpoint, such as /api/ai-reply.
    3. Your backend validates the request, rate-limits it and reads the AI key from a server-side secret.
    4. Backend calls the AI provider.
    5. Backend returns only the response your visitor needs.

    An unsafe architecture looks like this:

    // Do not do this in browser code.
    fetch("https://api.example-ai-provider.com/v1/responses", {
      headers: {
        Authorization: "Bearer sk-real-key-here"
      }
    });
    

    If the key is in browser code, the question is not whether visitors can see it. They can. The only question is how quickly someone will find and misuse it.

    3. Choose the right storage location for your host

    There is no single storage method that fits every hosting stack. Use the strongest option your platform supports, and document where each secret lives.

    Storage option Good use Main risk Practical check
    Host or platform secret store Production app hosting, serverless functions, workers, CI/CD Misconfigured access or wrong environment scope Confirm the secret is available only to the production service that needs it
    Environment variable Small server apps, VPS deployments, containers Debug tools, crash reports or process dumps may expose it Search logs for the variable value and avoid printing process.env
    Cloud secret manager Multi-service apps, teams, regulated or high-risk systems Requires identity and access management discipline Grant read access only to the service identity that needs the secret
    Protected config file Legacy PHP or WordPress setups File permissions, backups and accidental web exposure Keep it outside public web root where possible and restrict read permissions
    CMS/plugin database field Plugin-only integrations Admin users, compromised plugins, exports and backups may reveal it Use only if the plugin has no safer method and the site risk is low

    Heroku describes config vars as environment-specific configuration stored outside source code, exposed to app code as environment variables, and warns against direct references to sensitive variables where output may be written to logs. (devcenter.heroku.com) Cloudflare Workers has a separate concept of secrets for sensitive values such as API keys and auth tokens, and its docs also warn to add local .dev.vars* and .env* files to .gitignore. (developers.cloudflare.com) Vercel supports sensitive environment variables that are stored in a non-readable format once created. (vercel.com)

    For larger or higher-risk projects, a cloud secret manager can add better access control, auditability and rotation workflows. Google Cloud’s Secret Manager best practices emphasize least privilege, separating staging and production environments, secret-level access controls, rotation and access logging; it also warns that secrets passed through files or environment variables can leak through directory traversal, debug endpoints or dependencies that log process details. (docs.cloud.google.com)

    4. WordPress and CMS setups need extra caution

    WordPress sites often add AI features through plugins. That is convenient, but it changes your threat model: the plugin, WordPress administrators, database backups, debug logs and other plugins may all become part of the secret’s exposure surface.

    Use this order of preference:

    1. Best: plugin supports reading the key from an environment variable or a constant in wp-config.php.
    2. Acceptable for many small sites: plugin stores the key in its settings table, but access is restricted to trusted administrators and backups are protected.
    3. Avoid: key pasted into theme files, custom JavaScript, shortcode content, page builder blocks, analytics tags or frontend templates.

    A WordPress AI plugin setup might look like this:

    // wp-config.php, not a theme file.
    define( 'MY_AI_PROVIDER_API_KEY', getenv( 'OPENAI_API_KEY' ) );
    

    Then configure the plugin, custom integration or small must-use plugin to read MY_AI_PROVIDER_API_KEY on the server. If your host does not support environment variables, you may place the secret directly in wp-config.php, but protect the file carefully. WordPress hardening guidance says wp-config.php can be stored one directory above the WordPress installation and should be readable only by you and the web server, commonly permissions such as 400 or 440. (developer.wordpress.org)

    Also disable unnecessary file editing in the WordPress dashboard. WordPress notes that administrators can edit PHP plugin and theme files by default, and that adding define( 'DISALLOW_FILE_EDIT', true ); to wp-config.php removes those editing capabilities from users. (developer.wordpress.org) This does not make a compromised administrator harmless, but it reduces one easy path from admin access to code execution and credential exposure.
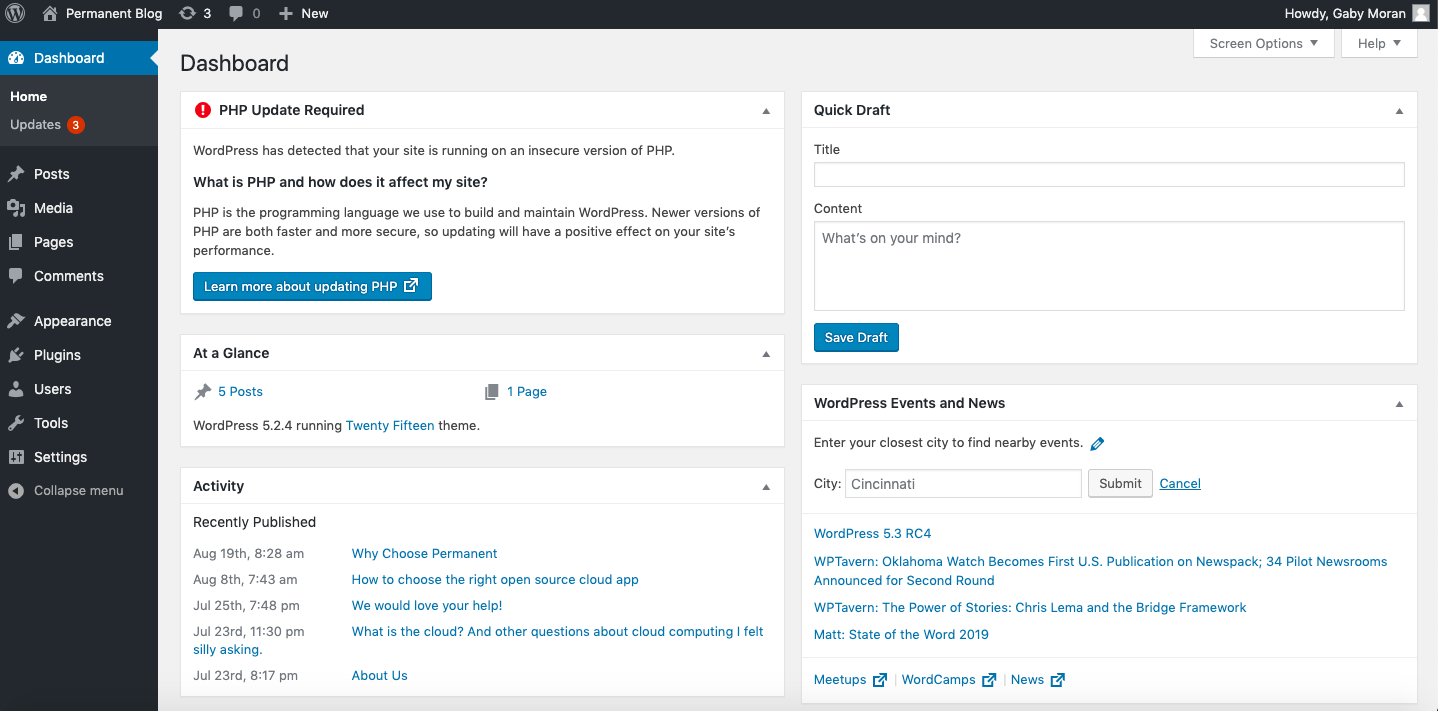
    Screenshot of a WordPress dashboard interface.
    WordPress dashboard context for configuring plugins without exposing API keys in public code. — Gmoran6. Own work Source CC BY-SA 4.0

    5. Backend route example: call the AI API without exposing the key

    Here is the pattern for a small Node backend. The key is read from the server environment. The browser never receives it.

    import express from "express";
    import OpenAI from "openai";
    
    const app = express();
    app.use(express.json());
    
    const openai = new OpenAI({
      apiKey: process.env.OPENAI_API_KEY
    });
    
    app.post("/api/ai-summary", async (req, res) => {
      const input = String(req.body.text || "").slice(0, 4000);
    
      if (!input) {
        return res.status(400).json({ error: "Text is required." });
      }
    
      try {
        const response = await openai.responses.create({
          model: "gpt-4.1-mini",
          input: `Summarize this for a website editor:\n\n${input}`
        });
    
        res.json({ summary: response.output_text });
      } catch (error) {
        // Log a request ID or safe error code, not headers or environment variables.
        console.error("AI request failed", { message: error.message });
        res.status(502).json({ error: "AI request failed. Try again later." });
      }
    });
    

    The same principle works in Python: read the value with os.environ["OPENAI_API_KEY"], call the AI provider from the server, and return a sanitized response. Anthropic’s API key guidance similarly recommends environment variables and cloud secret management, and says local .env files should be ignored by source control; in cloud environments it recommends encrypted secret storage rather than dotenv files. (support.anthropic.com)

    Before deploying this route, add:

    • Authentication or abuse controls if the endpoint can spend money.
    • Rate limits per user, session or IP address.
    • Request size limits.
    • Safe error messages.
    • A billing or usage alert at the AI provider if available.
    • Separate keys for development, staging and production.

    6. Permissions, rotation and logging hygiene

    Protecting secrets is not only about where they are stored. It is also about who can read them, what they can do and how quickly you can replace them.

    Use least privilege. OWASP’s Secrets Management Cheat Sheet says engineers should not have access to all secrets and that secret management systems should support fine-grained access controls. (cheatsheetseries.owasp.org) For a website, that means:

    • Give the production app only the production AI key it needs.
    • Do not reuse the same key across all client sites.
    • Do not give a WordPress plugin a key with account-wide administrative privileges if a narrower key is available.
    • Use different secrets for local development, staging and production.
    • Remove access when a developer, agency, plugin or integration no longer needs it.

    Logging needs the same discipline. OWASP’s logging guidance includes security-relevant events such as changes to privileges, assigning users to tokens and use or rotation of cryptographic keys as events worth logging. (cheatsheetseries.owasp.org) But logs should not contain the secret value itself. Avoid logging full request headers, full environment dumps, database connection strings, webhook payloads containing signatures, or complete exception objects from SDKs unless you have confirmed they are redacted.

    Common logging mistakes:

    • Printing process.env or $_ENV during debugging.
    • Returning provider error details directly to the browser.
    • Leaving WordPress debug display enabled on production.
    • Logging Authorization headers in reverse proxies.
    • Sending raw webhook requests to third-party observability tools.

    A useful check is to search your logs for the first and last six characters of each key. If you find a real key, rotate it.

    7. What to do if a key leaks

    Act as if the exposed key was copied. Do not wait to see abuse.

    Leaked-key response checklist:

    1. Revoke or rotate the exposed key immediately. OWASP lists immediate revocation and fast rotation as core exposure responses. (cheatsheetseries.owasp.org)
    2. Create a replacement key with the minimum permissions needed.
    3. Update every place that used the old key: host secret store, CI/CD variables, WordPress config, worker secrets, background jobs and local .env files.
    4. Redeploy or restart services if your host requires it for new environment variables to take effect.
    5. Review provider usage, billing and access logs for unusual requests after the likely exposure time.
    6. Remove the secret from the exposed location: current code, old commits where practical, logs, support tickets, screenshots and documentation.
    7. Scan the repository and history. GitHub secret scanning scans Git history for hardcoded credentials and recommends rotating affected credentials immediately when an alert is received. (docs.github.com)
    8. Write down the cause: browser bundle, plugin setting, debug log, support ticket, copied .env, public repo, backup archive or mis-scoped platform variable.
    9. Add a prevention control: .gitignore, pre-commit secret scanning, safer plugin configuration, restricted logs, separate environments or a proper secret manager.

    GitHub’s alert-resolution guidance also recommends reviewing and updating services that use the old token and checking security logs for unauthorized activity, depending on the provider. (docs.github.com)

    Pre-launch secrets audit

    Run this table before shipping an AI feature, chatbot, automation workflow or webhook integration.

    Check Pass condition
    Browser bundle No AI keys, database URLs, webhook secrets or private tokens in built JS, HTML source or source maps
    Repository .env, .dev.vars, private keys and config files with real secrets are ignored and absent from Git history
    Host settings Secrets are stored in platform secrets, sensitive env vars or a secret manager, not in public config
    WordPress/CMS Plugin keys are not in theme files, page content, custom JS or screenshots
    Permissions Production service can read only the secrets it needs
    Environments Development, staging and production use separate keys
    Logs Errors, headers, webhook payloads and environment dumps are redacted
    Backups Database and file backups containing secrets are access-controlled
    Rotation You know how to revoke, replace, deploy and verify each key
    Abuse controls Public endpoints that spend AI credits have rate limits and safe error responses

    Read next: How to Choose Hosting for an AI-Assisted Website Project
  • How to Choose Hosting for an AI-Assisted Website Project
    How to Choose Hosting for an AI-Assisted Website Project

    How to Choose Hosting for an AI-Assisted Website Project

    Answer box:
    Choose hosting for an AI-assisted website by matching the host to the work your site actually performs: normal web traffic, API calls, background jobs, database writes, file storage, secrets, logs, backups and staging. If your site only calls a hosted AI API from a plugin or backend, you usually do not need GPU hosting. You need reliable PHP, Node or Python support, secure environment variables, outbound HTTPS, rate-limit handling, cron or queue support, backups, logs and a way to cap both hosting and AI API spend. If your project trains or serves models itself, that is a different infrastructure decision and may require GPU or specialized compute.

    1. Choose for the workload, not the “AI” label

    An “AI website” can mean several different things. A WordPress blog that uses an AI writing assistant has very different hosting needs from a SaaS product running scheduled data enrichment jobs or a chatbot that sends every visitor message to an external model API.

    Start by placing your project in one of these buckets:

    Project type What matters most Hosting direction
    Small WordPress blog using AI content tools WordPress compatibility, plugin safety, backups, editor performance, secure API keys Managed WordPress or reliable shared/VPS hosting that meets current WordPress requirements
    Startup landing page with chatbot integration Fast frontend, secure backend API route, usage caps, logs, abuse controls Static/app hosting plus serverless or small backend
    Developer project with scheduled automation Cron jobs, queues, runtime limits, retry behavior, logs, database writes VPS, app platform, worker platform or serverless with documented scheduled jobs

    For WordPress, check the basics before anything else: WordPress currently recommends PHP 8.3 or greater, MariaDB 10.11 or greater or MySQL 8.0 or greater, and HTTPS support. It also notes that older PHP/MySQL versions may still work but have reached official end of life and may expose sites to security vulnerabilities. (wordpress.org)

    The key point: hosted AI APIs move the model computation to the API provider. Your host still has to run your site, protect credentials, call APIs reliably, store results where appropriate and stay observable when something fails.

    2. Map traffic and compute separately

    Do not estimate hosting from page views alone. Split the workload into:

    • Page delivery: HTML, CSS, images, JavaScript, CMS rendering and caching.
    • Interactive requests: search, forms, chatbot messages, account actions and webhook handlers.
    • AI API calls: requests sent to providers such as OpenAI or another model platform.
    • Background work: scheduled imports, summaries, batch tagging, newsletters, image processing or cache warming.
    • Database writes: posts, comments, user records, logs, embeddings, chat transcripts or job state.

    A useful rule is to avoid making a visitor wait for work that can safely happen later. For example, a blog post editor may request a summary immediately because the editor is waiting. A nightly “summarize all new comments” task belongs in a background job.

    For performance checks, use both lab and real-world evidence. Google’s Web Vitals guidance explains that lab data and real-user monitoring can differ because device type, network conditions, location, redirects, personalization and other factors vary. It also notes that some metrics, such as INP, require real user interactions and cannot be fully measured in a lab-only run. (web.dev)

    Practical check: before buying a plan, write down the slowest acceptable user action. “Homepage should load quickly” is too vague. “Chat response request should not block checkout,” “editor AI button can show a spinner,” or “nightly import can finish before 6 a.m. UTC” is actionable.

    A row of computer servers mounted in a data center rack.
    Server racks illustrate the underlying infrastructure behind hosting decisions. — , CSIRO. http://www.scienceimage.csiro.au/image/2042 CSIRO Source CC BY 3.0

    3. Treat API-driven AI as a reliability and cost problem

    If your site calls an external AI API, the most important hosting feature is often not CPU. It is safe, controlled outbound API access from a backend environment.

    OpenAI’s rate-limit documentation describes limits in requests per minute, requests per day, tokens per minute, tokens per day and other model-specific units. It also states that limits are defined at organization and project level, vary by model, and can be checked in the account limits area. (developers.openai.com)

    That means your hosting plan should support:

    • backend routes or server-side functions, not only browser-side scripts;
    • environment variables or a secrets manager for API keys;
    • request timeouts and retry logic;
    • logs that show failed API requests without exposing secrets;
    • spend controls or alerts in both the hosting platform and AI provider account.

    OpenAI’s production guidance recommends storing API keys securely, exposing them to applications through environment variables or a secret management service, and avoiding hard-coded keys. (developers.openai.com) Its API key safety guidance also says not to deploy keys in browser or mobile client-side environments because exposed keys can be used by others to make requests on your behalf. (help.openai.com)

    Common mistake: putting an AI API key into frontend JavaScript because it “works” during testing. If a user can view the key in browser developer tools, the key is exposed. Put the call behind your own backend endpoint and add basic abuse controls such as authentication, rate limits, CAPTCHA for public forms where appropriate and per-user quotas.

    4. Verify cron jobs, queues and background task limits

    Automation is where many AI-assisted projects outgrow basic hosting. A host may serve pages well but still be poor for scheduled jobs.

    Traditional control panels can expose cron jobs. cPanel’s support documentation describes creating cron jobs through the Cron Jobs icon under the Advanced section, if the hosting provider has enabled the feature, and shows common schedule presets such as “Once per 5 minutes.” (support.cpanel.net) App platforms and edge platforms may provide their own scheduled functions: Cloudflare Workers Cron Triggers map a cron expression to a Worker scheduled handler, execute on UTC time, and may take up to 15 minutes to propagate trigger changes globally. (developers.cloudflare.com) Vercel supports cron jobs for Vercel Functions and says they can be added through vercel.json or the Build Output API; its cron documentation also states that Vercel cron jobs use UTC and do not support alternative expressions such as MON, SUN, JAN or DEC. (vercel.com)

    Ask these questions before choosing a host:

    • What is the minimum schedule interval?
    • What is the maximum job duration?
    • Can two copies of the same job overlap?
    • Are failed jobs retried automatically?
    • Where do stdout, stderr and application logs go?
    • Can the job call external APIs?
    • Are scheduled jobs included in the plan or billed separately?

    Worked example: suppose a developer project checks 200 URLs each morning, sends changed pages to an AI API for summaries, then stores results in a database. A poor design runs everything in one web request and retries immediately when the API returns a rate-limit error. A better design stores a job queue, processes a safe batch size, records progress, respects Retry-After or exponential backoff guidance, and resumes later if the platform time limit is reached. OpenAI’s rate-limit guidance says a 429 response can include a Retry-After header and that callers should wait at least that long, with a small random delay to avoid synchronized retries. (developers.openai.com)

    5. Size storage and databases for the data you keep

    AI features often create extra data even when the model runs elsewhere. Examples include prompts, outputs, moderation results, cached summaries, transcripts, embeddings, uploaded files, generated images and job logs.

    Before selecting hosting, decide what you will store and for how long:

    • CMS content: posts, pages, revisions, media library files.
    • Operational data: job state, webhook receipts, error logs.
    • User data: chat messages, support requests, account metadata.
    • AI artifacts: summaries, tags, embeddings, generated images or uploaded documents.
    • Backups: database dumps, file backups and offsite copies.

    Do not keep sensitive prompts or customer data “just in case.” If you do keep AI interaction history, make sure your database plan, privacy disclosures and deletion process match that decision. For a small WordPress site, the immediate database question may simply be whether the host meets WordPress’s supported PHP and database versions. For an app, ask about database connection limits, storage growth, point-in-time recovery, read replicas if needed and export options.

    Practical check: estimate storage by data category, not as one lump. Media files, database rows and backups grow differently. A host with “generous storage” may still restrict database size, inode count, backup retention or object storage bandwidth.

    6. Require security controls for API keys and admin access

    AI-assisted sites tend to collect powerful credentials: hosting logins, CMS admin accounts, deployment tokens, AI API keys, database passwords and webhook signing secrets. Hosting should help you reduce the blast radius of a mistake.

    Minimum controls to look for:

    • environment variables or secret storage;
    • separate production and staging secrets;
    • role-based access for team members;
    • SSH or SFTP access that can be limited and rotated;
    • two-factor authentication for the hosting account;
    • TLS/HTTPS support;
    • audit logs or login history where available;
    • easy key rotation after a leak.

    OpenAI’s API key safety guidance recommends unique keys for each team member, key expiration and rotation, avoiding repositories, using environment variables, and using a key management service where appropriate. (help.openai.com) OWASP’s secrets management guidance identifies API keys, database credentials, IAM permissions, SSH keys and certificates as secrets and emphasizes centralized storage, auditing, rotation and access control. (cheatsheetseries.owasp.org)

    Also check terms. OpenAI’s services agreement prohibits, among other things, buying, selling or transferring API keys and interfering with or circumventing rate limits, restrictions, protective measures or usage limits. (openai.com) Hosting providers and automation platforms have their own acceptable-use rules too, so confirm that scraping, bulk email, bot activity, background automation or public chatbot use is allowed for your plan.

    7. Use staging, backups and logs before production changes

    AI tools can speed up site operations, but they can also generate wrong commands, unsafe code or changes that look plausible and fail later. Treat AI-assisted deployment like any other risky production change: test, back up and keep rollback options.

    A good host for AI-assisted operations should provide:

    • a staging environment or a safe way to clone the site;
    • version-controlled deployment where possible;
    • backup creation before major changes;
    • restore testing, not just backup creation;
    • web server logs and application logs;
    • error monitoring or at least downloadable logs.

    cPanel’s Backup Wizard documentation says the interface can back up all or part of a website and restore the most recent partial backup file, but it also notes that a full backup cannot be automatically restored in cPanel and that users should contact the hosting provider for full-backup restoration through WHM. (docs.cpanel.net) cPanel’s log file documentation also identifies where webserver log data for user accounts is stored and describes log rotation and archive behavior. (docs.cpanel.net)

    Common mistake: assuming “daily backups” means easy recovery. Ask whether backups include files and databases, how long they are retained, whether they are stored off-server, whether you can restore a single database, and whether restoring overwrites newer user content.

    8. Put cost limits and provider terms in the checklist

    AI hosting decisions can fail financially even when the architecture works. Costs may come from hosting, serverless invocations, bandwidth, database storage, log retention, object storage, scheduled jobs and AI API usage.

    OpenAI’s pricing page shows that API usage can be billed by tokens, tool calls, storage, hosted containers, web search calls or other model/tool-specific units depending on what you use. (developers.openai.com) Its production guidance also recommends spend alerts and hard spend limits, while warning that hard spend limits can stop affected API traffic when tracked spend reaches the limit. (developers.openai.com)

    Use this purchase checklist:

    1. Runtime: Does the host support your stack: WordPress/PHP, Node, Python, containers or static frontend plus backend functions?
    2. Secrets: Can API keys be stored outside code and outside the browser?
    3. Outbound API calls: Are external HTTPS calls allowed, and are timeouts long enough?
    4. Background work: Are cron jobs, queues or workers supported with documented limits?
    5. Database: Are version, storage, connection and backup features adequate?
    6. Staging: Can you test plugins, prompts, code and migrations safely?
    7. Logs: Can you inspect failed jobs, API errors and suspicious access?
    8. Backups: Can you restore files and databases separately, and have you tested it?
    9. Costs: Can you set alerts or caps for hosting and AI API usage?
    10. Terms: Do the host and AI provider permit your automation, user content and traffic pattern?

    The best hosting plan is not the one with the biggest “AI” badge. It is the one that lets your site run its real workload safely: serve pages, protect secrets, call APIs responsibly, process background jobs, recover from mistakes and keep costs inside limits you can live with.

  • Website Deployment Checklist Before Changing DNS or Migrating Hosts

    Website Deployment Checklist Before Changing DNS or Migrating Hosts

    Answer box: What should I verify before I move a live site or point DNS to a new host?
    Before changing DNS, verify that you have a current restorable backup, a tested staging copy, a complete DNS inventory, a lower TTL plan, valid SSL/TLS coverage, working email records, a checked database import, a rollback path, and post-launch monitoring. Do not treat a successful file upload as a successful migration. A live site also depends on database writes, redirects, scheduled tasks, payment callbacks, mail delivery, certificates, cache rules and DNS records.

    Changing hosts is not one switch. DNS is only the cutover step. Google’s hosting-change guidance describes the basic sequence as preparing and testing the new infrastructure, changing DNS, then monitoring traffic on both old and new hosting. It also notes that temporary crawl-rate changes can happen after a hosting infrastructure change, so launch monitoring matters even when URLs stay the same. (developers.google.cn)

    1. Make a pre-migration inventory before you copy anything

    Start by writing down what currently serves the site. This is your control sheet for testing, rollback and support tickets.

    Record:

    • Domain registrar and authoritative DNS provider.
    • Current nameservers.
    • Existing DNS records: A, AAAA, CNAME, MX, TXT, CAA, SRV and any subdomain records.
    • Current host, server IPs, control panel, SSH/SFTP details and deployment method.
    • CMS version, theme, plugins, extensions and custom code.
    • Runtime requirements: PHP, Node, Python, Ruby, database version, web server, memory limits and cron jobs.
    • Upload directories, media storage, private files and environment variables.
    • CDN, WAF, caching, redirects and page rules.
    • Email provider and authentication records.
    • Analytics, search console, tag manager, payment gateway and webhook endpoints.
    • Forms, transactional email, background queues and scheduled tasks.

    The inventory should identify what must move and what must stay. For example, you may move the website but keep DNS with the current DNS provider. Or you may move hosting and DNS but keep email with the same mail provider. Mixing those up is a common cause of avoidable outages.

    For WordPress, inventory both files and database. WordPress documentation explains that a WordPress site includes files such as core, themes, plugins, uploads and configuration files, while the database stores posts and much generated site data; downloading the WordPress directory alone usually does not back up the database. (developer.wordpress.org)

    2. Verify backups by restoring, not just downloading

    A backup is only useful if you can restore it. Before the migration window, create a backup set that includes:

    • Site files.
    • Database export.
    • Configuration files such as .htaccess, wp-config.php, server redirects and environment files.
    • Media/uploads.
    • Any private storage outside the web root.
    • DNS zone export or screenshots.
    • Email routing records.
    • A note of current server IPs and hostnames.

    WordPress guidance says to back up the database and files before moving WordPress to a new server, and its backup documentation describes a typical backup order of database first, then files; restore is typically files first, then database import. (developer.wordpress.org) (developer.wordpress.org)

    Do at least one restore test in a non-production location. That may be a staging subdomain, local container or temporary host URL. Check that the restored site can load key pages, access the admin area, show images and connect to the database.

    For higher-risk sites, keep more than one backup location. CISA-backed backup guidance commonly describes the 3-2-1 model: keep three copies of important data, on two different media types, with one copy offsite. (cisa.gov)

    Practical check: name the backup folder with the date, site name and source host. Keep the database export in the same migration package as the matching files so you do not import a database from Tuesday with uploads from Thursday.

    Three external hard drives on a desk representing backup storage.
    A migration backup should include both site files and the matching database export. — TonyTheTiger. Own work Source CC BY-SA 3.0

    3. Build and test staging before lowering the drawbridge

    Do not point live DNS at a new host that you have only viewed through a control panel preview. Test the new environment as close to production as you safely can.

    Minimum staging checks:

    • Homepage, important landing pages and recent posts.
    • Login, password reset and admin pages.
    • Contact forms and transactional email.
    • Search, filters, carts or account areas.
    • Image uploads and media paths.
    • Redirects and canonical URLs.
    • XML sitemap and robots rules.
    • 404 page behavior.
    • Cron jobs, queues and scheduled publishing.
    • Error logs under real requests.
    • Mobile layout and core templates.
    • Cache purge process.

    If the site is on WordPress and the domain stays the same, WordPress says moving files and database may be enough when the database and URL remain the same, but wp-config.php must be updated if database name, user or host changes. It also warns that URL changes inside the database can cause issues with serialized data if handled by a careless search-and-replace. (developer.wordpress.org)

    Use your local hosts file, a temporary staging domain or provider preview domain to test the new server before DNS cutover. If you use a staging domain, be careful with noindex settings and robots rules. Google’s hosting-change guidance specifically says to remove temporary crawling blocks such as robots.txt disallows or noindex controls before starting the move. (developers.google.cn)

    4. Plan DNS TTL, records and cutover timing

    TTL, or Time to Live, controls how long DNS records may be cached. Cloudflare’s DNS documentation explains that longer TTLs can make lookups faster because cached answers are reused, but longer TTLs also mean record updates take longer to take effect. (developers.cloudflare.com)

    A practical plan:

    1. Two or three days before launch, list current DNS records.
    2. Lower TTLs for records you expect to change, such as the root A record and www record, if your DNS provider allows it.
    3. Do not delete old records until you know what they do.
    4. Prepare the new records but do not publish them early unless you understand the effect.
    5. At launch, change only the necessary records.
    6. Keep the old host active during propagation and rollback period.

    Cloudflare notes that proxied records use an automatic TTL set to 300 seconds, while DNS-only records can have configurable TTLs within provider limits. It also cautions that local DNS cache may make changes appear slower to an individual user than the record TTL suggests. (developers.cloudflare.com)

    Common mistake: changing nameservers and host records at the same time without exporting the old zone. If you move DNS providers, all required records must exist at the new DNS provider before the registrar points to it. That includes records for email, verification, CDN, payment services and subdomains—not just the website IP.

    Practical check: use more than one DNS lookup source after launch. Google also recommends using public DNS checking tools and watching traffic move from old servers to new servers during a hosting change. (developers.google.cn)

    5. Confirm SSL/TLS before live traffic arrives

    A new host needs a certificate that matches every public hostname you will serve, commonly the root domain and www. If the old host had HTTPS, the new host must be ready for HTTPS before you send users there.

    Check:

    • Certificate covers all required hostnames.
    • HTTP redirects to HTTPS work as intended.
    • Mixed content warnings are absent.
    • HSTS settings are understood before launch.
    • CDN and origin TLS modes are compatible.
    • Renewal automation works on the new host.
    • Port 80 or DNS validation requirements are met.

    Let’s Encrypt explains that certificate issuance requires proving control of the domain through ACME challenge types. HTTP-01 is often handled automatically by an ACME client, while DNS-01 requires placing a TXT value under _acme-challenge and is useful for cases such as wildcard certificates. Let’s Encrypt also warns that DNS validation automation should avoid broad DNS API credentials on a web server when possible. (letsencrypt.org)

    Common mistake: waiting until after DNS cutover to request a certificate, then discovering the new host cannot validate because traffic is still cached toward the old host, port 80 is blocked, or the DNS provider API is not configured.

    Practical check: browse the staging site over HTTPS, inspect the certificate hostname and expiry, and test both https://example.com and https://www.example.com equivalents before launch.

    6. Protect email routing and third-party callbacks

    Many migrations break email because the person moving the site copies only web records. Email may be handled by a separate provider and usually depends on DNS records that should not be replaced by the web host’s defaults.

    Verify:

    • MX records still point to the intended mail provider.
    • SPF TXT record includes the correct sending systems.
    • DKIM selectors still exist.
    • DMARC record remains in place.
    • Web forms send through an approved SMTP or mail API.
    • Transactional messages do not rely on blocked local PHP mail.
    • Any domain verification records for email platforms remain present.

    Cloudflare’s email DNS documentation explains that MX records are used for receiving email through the selected provider, and that SPF, DKIM and DMARC records help receiving mail servers verify messages and reduce spoofing risk. It also notes that exact mail record values depend on the email provider. (developers.cloudflare.com)

    For ecommerce and membership sites, also list callbacks and webhooks. WooCommerce payment gateway documentation describes callbacks where a gateway calls a store URL to report order status. If those callback URLs fail after migration, payments and order updates may not reconcile correctly. (developer.woocommerce.com)

    Practical check: after staging, send a contact form message, a password reset, a test order email and any relevant transactional message to an external inbox. For ecommerce, use the payment provider’s sandbox or test mode where available, and confirm webhook delivery logs.

    7. Check database export/import and app configuration

    Database migrations fail in quiet ways. A site may load while recent orders, user accounts, media references or serialized settings are missing.

    For database-backed sites, verify:

    • Export completed without errors.
    • Import completed without errors.
    • Character set and collation are compatible.
    • Table counts are plausible.
    • Recent records exist.
    • Application config points to the new database host, name, user and password.
    • Read/write actions work, not only read-only page views.
    • No hardcoded paths still point to old server directories.

    MySQL documentation describes mysqldump as a way to create backup files and, with certain options, table data and CREATE TABLE statements. The exact export and import method should match your database engine, host limits and site size. (dev.mysql.com)

    Worked WordPress example:

    1. Put the old site into a low-change window, or pause publishing and orders if possible.
    2. Export the database.
    3. Copy files including wp-content/uploads, themes, plugins, .htaccess and wp-config.php.
    4. Import the database on the new host.
    5. Update wp-config.php only for the new database credentials.
    6. Test admin login, permalinks, media, forms and plugin functions.
    7. If the domain changes, use a WordPress-aware search-replace method rather than a raw text replacement that may break serialized data. WordPress specifically flags serialized data as a risk during URL replacements. (developer.wordpress.org)

    Worked static-site example:

    1. Build the production artifact from the same commit you intend to deploy.
    2. Upload to the new host or object storage.
    3. Confirm routes, redirects, custom error page, headers and cache rules.
    4. Check that forms, search and comments are not secretly dependent on the old host.
    5. Point DNS only after the preview URL or host-file test passes.

    Worked ecommerce example:

    1. Freeze catalog edits during the final sync.
    2. Export and import the database as close to launch as practical.
    3. Test checkout in sandbox mode.
    4. Confirm webhook or callback URLs are reachable.
    5. Confirm mail records and transactional email sending.
    6. Keep the old host available until payment, order and email logs show normal behavior.

    8. Write a rollback plan and monitor after launch

    Rollback should be written before launch, not invented during an outage.

    Your rollback note should say:

    • Which DNS records will be changed back.
    • What old IP or host target to restore.
    • Who has registrar, DNS, host and CMS access.
    • Where the last known-good backup is stored.
    • Whether database writes must be reconciled before rollback.
    • What condition triggers rollback.
    • Who decides.

    Rollback is simple for a static site if no data changed. It is harder for ecommerce, forums, learning platforms and booking systems because users may create data on the new host after launch. In those cases, plan a maintenance window, a write freeze or a clear decision about how new writes will be handled.

    After DNS cutover, monitor:

    • Uptime checks.
    • Server access and error logs.
    • DNS resolution for root and www.
    • HTTPS certificate status.
    • 404 and 500 errors.
    • Form submissions.
    • Email delivery.
    • Checkout or payment logs.
    • Search Console crawl and indexing reports.
    • Old server traffic falling and new server traffic rising.

    Google recommends keeping an eye on logs from both old and new servers as DNS propagation shifts traffic. That is one of the simplest ways to see whether users and crawlers are actually reaching the new infrastructure. (developers.google.cn)

    For high-risk migrations involving regulated data, payment data, security incidents or business-critical uptime, get qualified help. This article is general operational guidance, not a managed migration service or legal/security advice. See the site’s Disclaimer for the site’s general information limits.